
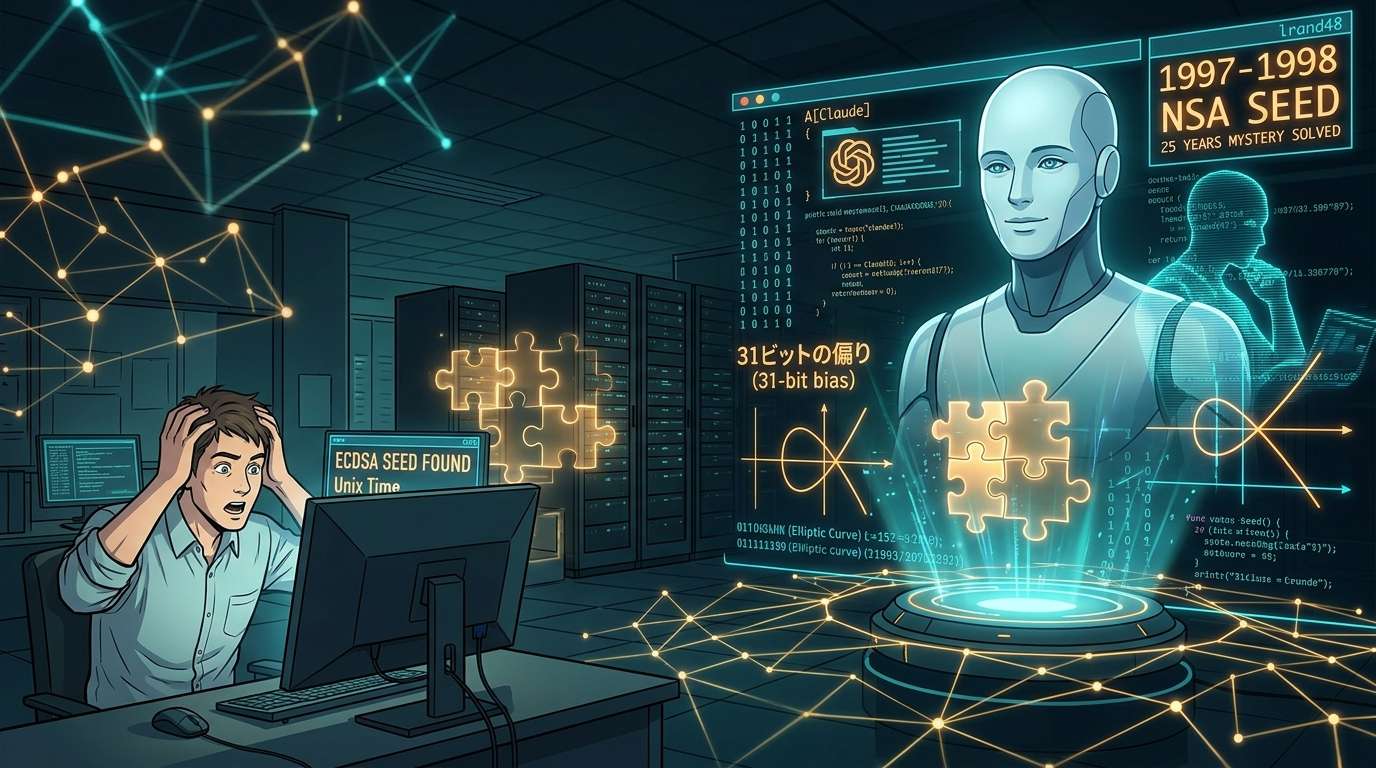
The origin of “seeds” provided by the U.S. National Security Agency (NSA) for ECDSA-related elliptic curves standardized by the National Institute of Standards and Technology (NIST) in 2000 remained unknown for about 25 years. Anthropic’s AI, Claude, reportedly found clues to how they were generated in less than 30 minutes. This was not a case of breaking the cryptography, but of uncovering the provenance of a set of parameters.
It didn’t break the cryptography; it solved a provenance puzzle
When you hear that AI has solved a cryptographic mystery, it’s easy to picture a dramatic scene in which it cracks a key. But this case was a little different. What was solved was not the security of the cryptography itself, but a question of provenance: “Where did this number come from?”
That’s what makes the story interesting. Rather than using brute force to break through, the AI used a small bias in the data as a clue and narrowed down the possibilities. This is an example of AI answering a question that had remained open for nearly 25 years.
A mysterious seed fuels suspicion
ECDSA is a widely used standard for digital signatures based on elliptic curves. The value used as a starting point when generating the curve parameters for this standard is called a “seed,” and the NSA provided it. But no explanation was given for how the value had been generated.
Think of it as a secret sauce with no recipe. It may taste good, but if no one knows what’s in it, some will wonder whether something has been slipped in. Configuration values with unclear origins have raised suspicions that an intentional backdoor might be hidden in them, prompting a cash reward and investigations by volunteers.
The late Jerry Solinas, a former NSA employee, had suggested that the seed might be a humorous phrase run through a hash function—a process that converts data into another value according to a set of rules—but that turned out to be wrong.
A 31-bit bias provided the clue
Claude focused on a pattern in some of the seeds: their upper bits were consistently zero. The seeds had been generated using lrand48, a simple random number generator in C. The initial values were reportedly Unix timestamps from between May 1997 and April 1998—the number of seconds elapsed since January 1, 1970.
The decisive clue was that lrand48 produces only 31 bits of output. If a 32-digit container holds a value of only 31 digits, the most significant digit will tend to be zero. The key was to interpret this bias not as an unnatural pattern, but as the fingerprint of a particular random number generator.
The speed—less than 30 minutes—also stands out. But that is only an estimate of the time spent on the task; it shouldn’t be discussed without accounting for the years of prior investigation and debate. I see the AI’s strength as its ability to focus, without preconceptions, on a clue that people had overlooked for years.
Uncovering the origin does not prove the system is secure
Anthropic reportedly said that this explanation makes the possibility of an intentional backdoor less likely. But “less likely” is not the same as “proven not to exist.” Identifying how the seed was generated is an important step forward, but it does not by itself guarantee the security of the curve as a whole.
Trust in cryptography rests not only on its strength, but also on whether third parties can verify the origins of its parameters. This case is a reminder that “unexplained numbers” can remain a source of suspicion for years.
The $36,864 reward offered for solving this mystery is reportedly being donated by Anthropic to the nonprofit Internet Security Research Group (ISRG).
Comments